A weak password was enough to bring down one of Britain's oldest transport companies. The KNP Logistics Group, a transport and logistics service provider with a 158-year history, became the target of a ransomware attack—with devastating consequences. According to media reports (Golem.de, BBC), the well-known hacker group Akira exploited the
poor security of an employee account to gain access to the company's network.
As a result, central IT systems were completely encrypted. Operations came to a standstill—affecting around 700 employees and over 500 vehicles in the commercial vehicle fleet.
In exchange for decrypting the IT systems, the attackers demanded a
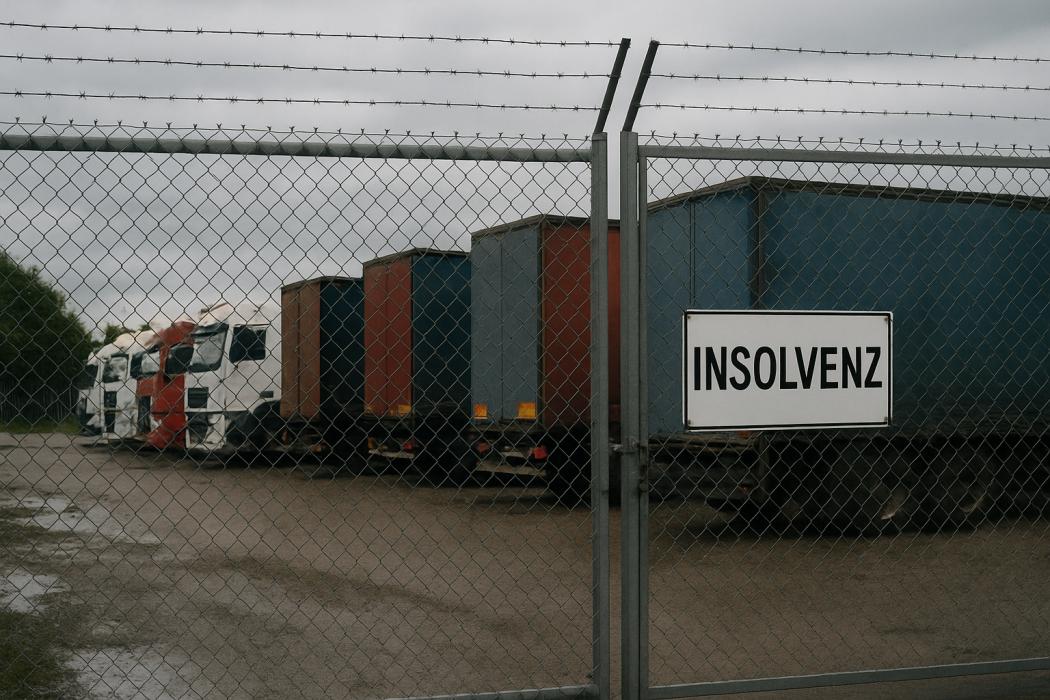
ransom of five million pounds (around 5.8 million euros). Since the freight company could not raise this amount and apparently had no functioning data backups, the company had no choice but to cease operations.
The traditional British company had to file for bankruptcy just a few days after the attack.
Industry experts see the incident as another wake-up call for the transport and logistics sector. Particularly, small and medium-sized enterprises (SMEs) are often targets of such attacks—often due to known inadequate cybersecurity:
Too simple passwords, lack of two-factor authentication, and insufficient backup strategies can quickly become a nightmare in a